The UKs #1 Data Protection Consultancy

Data Protection & Information Security Experts

Data Protection Made Easy.

GDPR Support Cyber Security Support
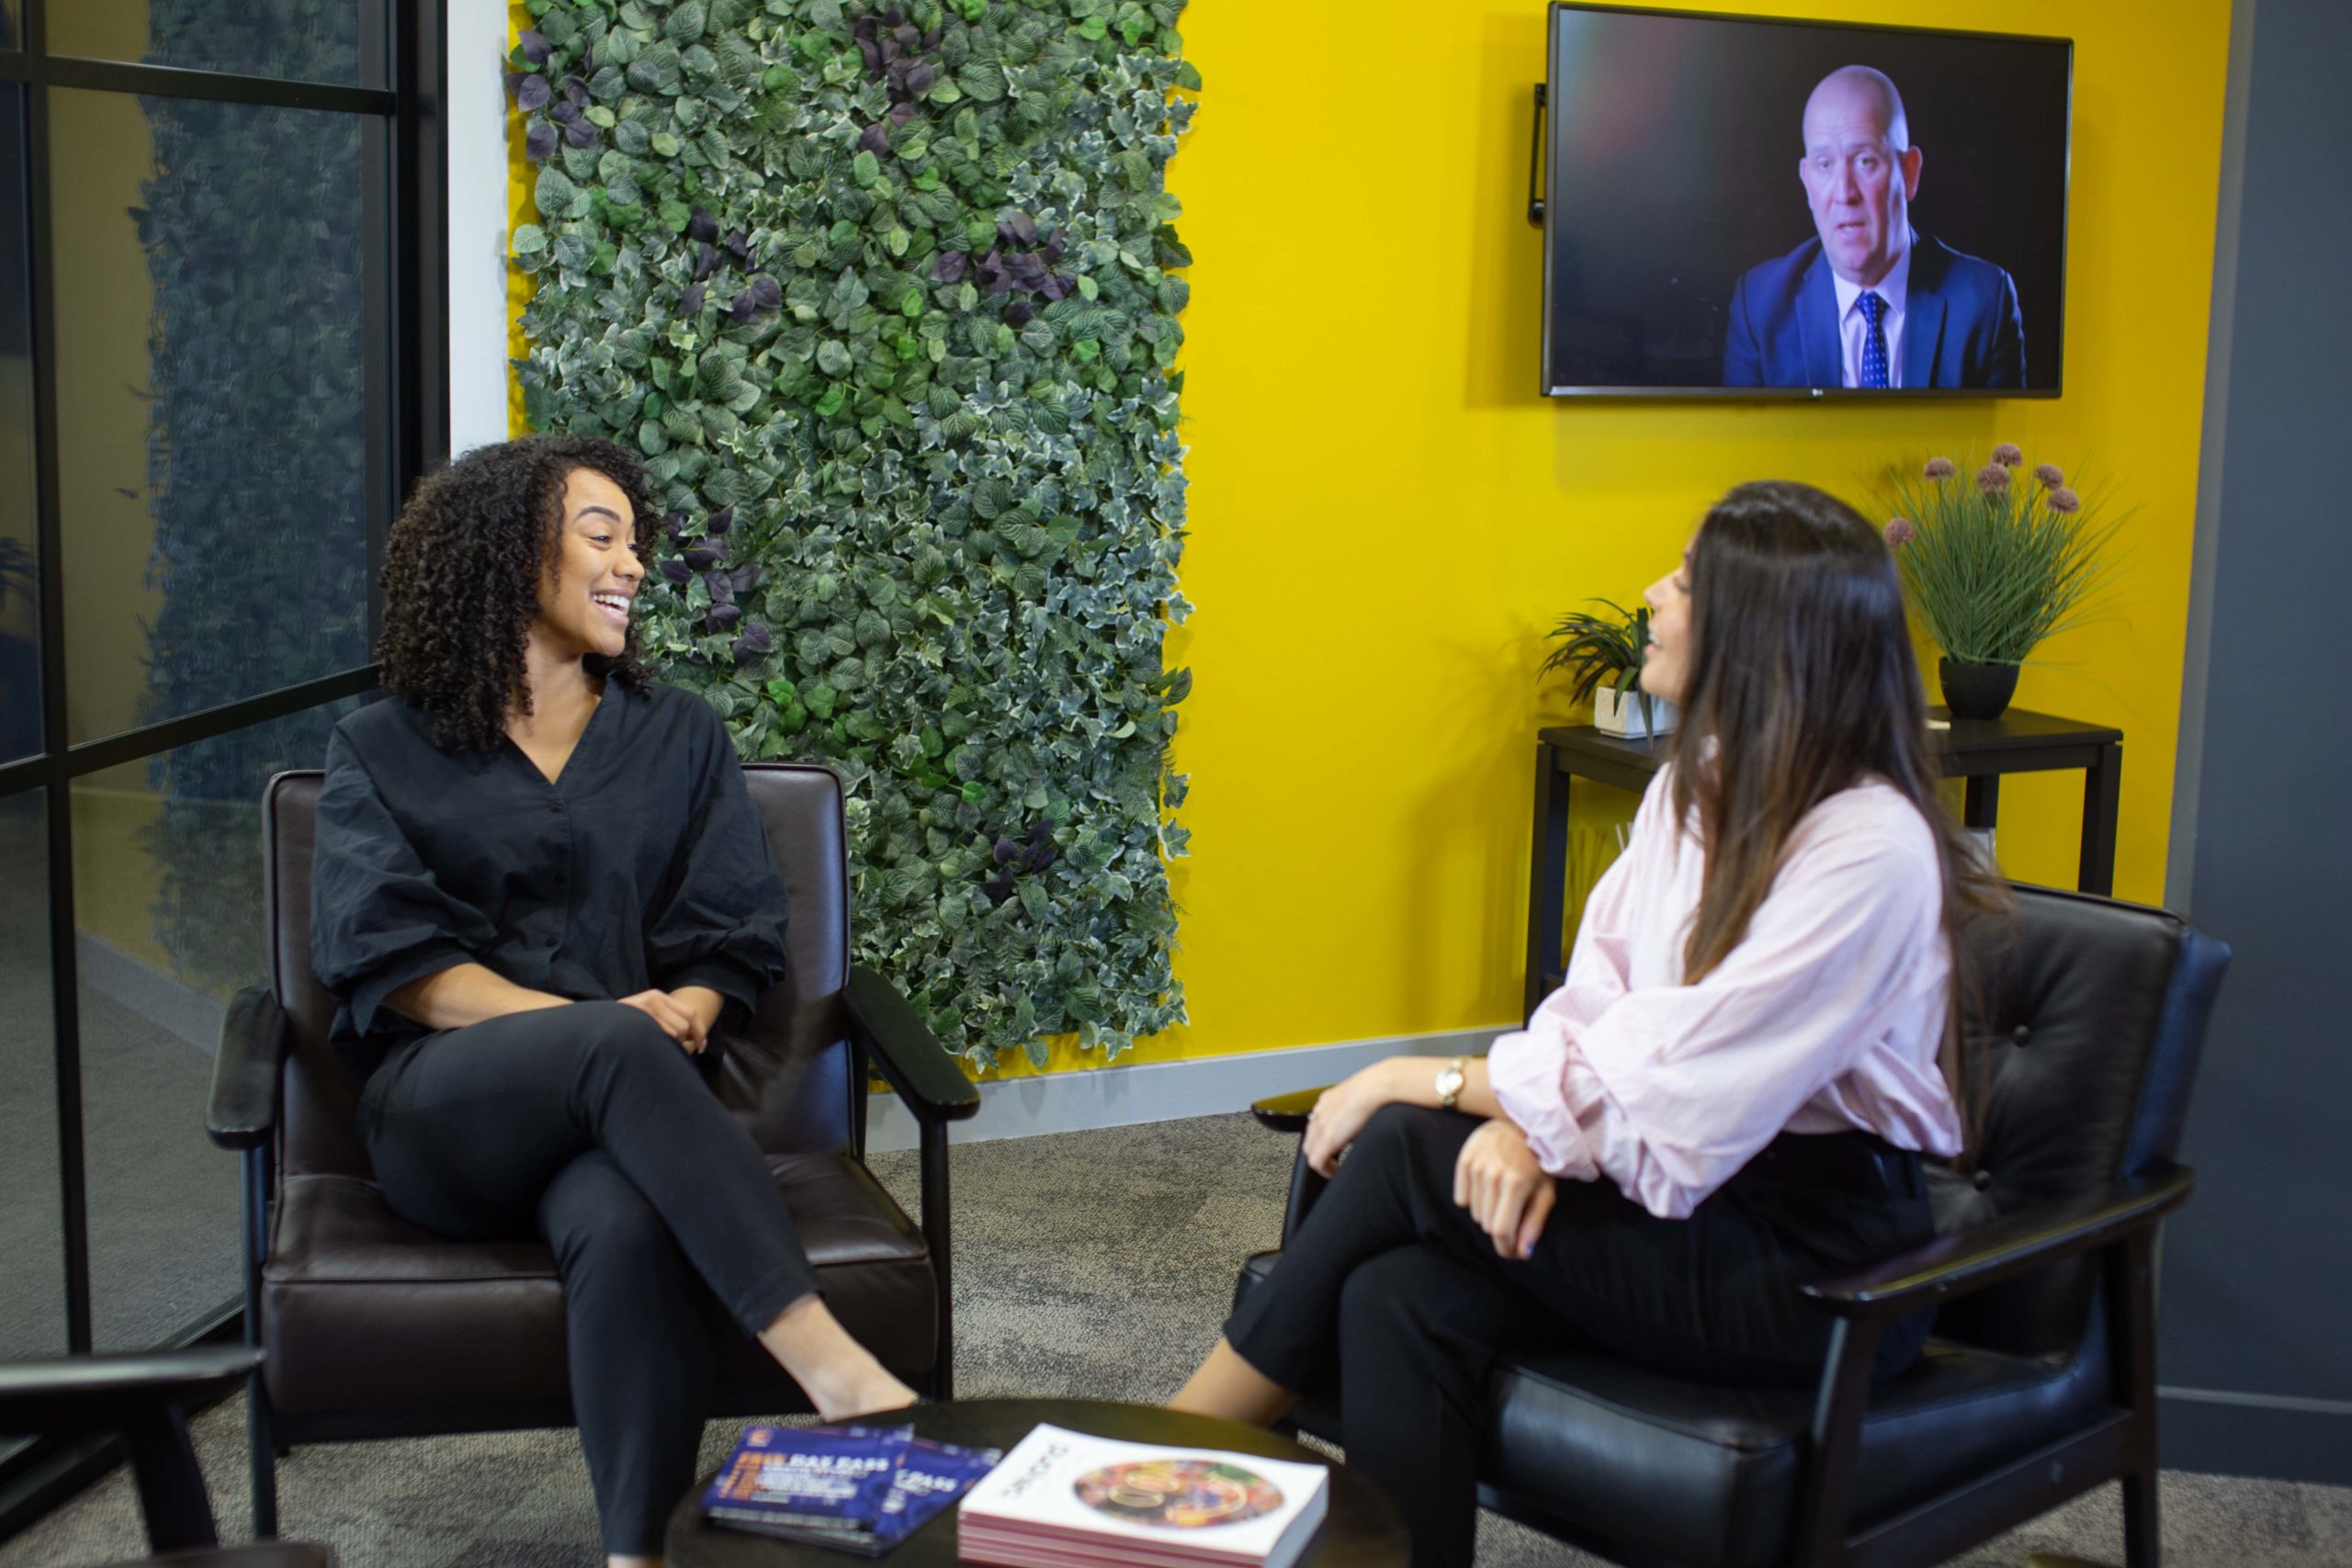
Cate and Jas Chatting
Join our extensive list of clients who have their data privacy under control

Accelerate Your Data Protection Compliance

Save Time, Save Money and Relax: You’re In Safe Hands

Discover the comprehensive range of data protection services at Data Protection People. Tailored to meet the unique needs of your organisation, our expert team has successfully handled every challenge imaginable. Whether you’re navigating compliance complexities or enhancing data security, trust DPP to be your partner in safeguarding information.

SAR Support

Explore our Subject Access Request (SAR) Handling Service and understand how Data Protection People can support your organisation

Contact Us

Data Protection Support

Data Protection People's world-class GDPR Support Desk. If you're navigating the complex landscape of data protection, PCI DSS, and cybersecurity, our support desk is your reliable compass.

Contact Us

Outsourced DPO

A data protection officer doesn't have to be a full time employee and in many respects it's better to have a company like DPP take on the role. Watch the video below to find out more about our outsourced DPO and privacy officer services or reach out and get in touch with us.

Contact Us

Data Protection Audit & GDPR Audit Services

A range of high level reviews, detailed audits and mid-range assessments to test compliance with data protection laws and standards

Contact Us
View All

Need Help With Cyber Security Compliance?

We Have You Covered!

At Data Protection People, our cyber security services are designed to fortify your digital defences. With a proven track record spanning diverse sectors in the UK, our seasoned team brings a wealth of experience in handling a wide array of cybersecurity challenges. Reach out to us and explore how DPP can enhance your organisation’s cyber resilience.

PCI DSS Compliance Services for Merchants

A PCI assessment is an audit for validating compliance with the Payment Card Industry Data Security Standard (PCI DSS), a set of security standards for merchants who accept, process, store or transmit credit card information.

Contact Us

PCI DSS Compliance Services for Service Providers

A PCI assessment is an audit for validating compliance with the Payment Card Industry Data Security Standard (PCI DSS), a set of security standards for merchants who accept, process, store or transmit credit card information.

Contact Us

External Attack Surface Management

Our experts can support you with Dark Web Monitoring - Data Protection People offer a free dark web scan for your organisation.

Contact Us

PCI DSS

A PCI assessment is an audit for validating compliance with the Payment Card Industry Data Security Standard (PCI DSS), a set of security standards for merchants who accept, process, store or transmit credit card information.

Contact Us
View All
Rofi Hendra Support Desk Data Protection People

Supporting DPOs

Flexible Support When You Need It

At Data Protection People, we recognise the dynamic challenges and unique responsibilities of the Data Protection Officer (DPO) role. Beyond offering standard support, we provide a comprehensive suite of services crafted to empower DPOs at every step.

Collaborative Community: Navigating the intricate landscape of data protection can be isolating. That’s why we’ve fostered a collaborative community of privacy professionals. As a DPO with us, you’re never alone. Our network serves as a forum for insightful discussions, sharing solutions, and building a sense of camaraderie.

Expert Guidance and Advice: The journey of a DPO is often filled with complex decisions. Our seasoned team of experts is your reliable resource, offering timely advice and strategic guidance. We’re not just a service provider; we’re your dedicated partners in overcoming challenges and making informed decisions.

Advanced Training for Continuous Growth: Stay ahead in your role with our advanced training programs. Tailored for DPOs, our courses delve into intricate aspects of data protection, providing you with a competitive edge. It’s not just about meeting the present challenges but ensuring your continuous growth and excellence in your role.

Audits, Assessments, and Document Reviews: Our services extend beyond conventional boundaries. From comprehensive audits and assessments to meticulous document reviews, we ensure that your data protection strategies are not only compliant but also optimised for efficiency.

Simplifying Complexity for Future Ease: Beyond addressing current challenges, our mission is to simplify the complexities inherent in data protection. By partnering with Data Protection People, you’re not just solving problems – you’re ensuring a smoother, more efficient role in the future. We streamline processes, making your responsibilities more manageable and your decisions more impactful.

Diverse Sector Experience

Access to a Team of Industry Experts

At Data Protection People, our expertise spans across diverse sectors, ensuring that businesses of all sizes and orientations receive tailored Data Protection and Cyber Security solutions. From the dynamic commercial sector and agile SMEs to the impactful third sector and expansive multi-nationals, we extend our services to fortify the digital defences of every business entity.

Skyline vertical

Commercial Sector

Elevate your data protection and cybersecurity standards in the bustling landscape of the Commercial Sector. We offer tailored solutions designed to safeguard your sensitive information, ensuring compliance and resilience against evolving threats. Partner with us to fortify your digital assets and foster a secure environment for sustained growth.

Card DPP Payment

SMEs

Small and Medium Enterprises (SMEs) form the backbone of innovation. Our data protection and cybersecurity services are crafted to match the agility of SMEs. Navigate the digital landscape securely, optimize your operations, and scale confidently with our tailored solutions that prioritize your unique business needs.

Third Sector

Third Sector

For organisations in the Third Sector driven by purpose, our data protection and cybersecurity expertise align with your mission. Safeguard sensitive data, build stakeholder trust, and amplify your positive impact. Let our solutions be the backbone of your technology infrastructure, ensuring that your focus remains on making a difference.

Boat in water

Multi Nationals

For the global footprint of Multi Nationals, our data protection and cybersecurity services provide a comprehensive shield. Navigate the complexities of international regulations with confidence. From compliance strategies to threat intelligence, we've got your data security needs covered, empowering your multinational endeavors with resilience.

Certification in cyber

Public Sector

In the Public Sector, trust and accountability are paramount. Our data protection and cybersecurity consultancy ensures that your operations align seamlessly with regulatory requirements. From confidential citizen data to streamlined governance, our solutions empower public entities to serve with integrity and technological excellence.

Caratina consulting

Why Use Our Outsourced DPO Services?

Save Time, Money and Guarantee Compliance

Navigating the intricate landscape of data protection demands more than just a DPO — it requires a dedicated team committed to excellence. Our Outsourced DPO Services extend beyond the traditional role, offering a comprehensive approach to legal compliance and pragmatic solutions.

Why Choose Outsourcing?

An outsourced DPO brings a wealth of experience, not just in the law but also in crafting workable solutions. Their impartiality is fortified by a team of privacy practitioners, ensuring that your organization benefits from a spectrum of expertise. Should the need arise, seamless coverage during absences is guaranteed, eliminating the vulnerability associated with a single in-house DPO.

Staying Headache-Free

Concerned about the disruption if your DPO moves on? With an outsourced model, transitions are smooth, and you won’t experience the sudden headache of a critical role vacancy. The continuity provided by a team ensures that your data protection responsibilities are seamlessly handled.

Compliance Tailored to You

Our Outsourced DPO Services align seamlessly with your legal obligations, whether you’re mandated to appoint a DPO or choose to do so voluntarily. We understand that compliance is not just about ticking boxes but about ensuring a robust, practical approach to data protection. Choose Data Protection People for a worry-free, compliance-driven outsourced DPO solution — because your data protection journey should be as smooth as it is secure.

eastlight housing

“I cant recommend Data Protection People enough, they have helped me in so many different areas, no matter how complex the challenge or how large the obstacle, DPP always has the answer.

I can call the team at any time and have built an amazing relationship with them, in times of frustration they are here to calm me down and create a plan, they are a pleasure to work with.”

Mark Leete
Eastlight Community Homes
TDC_logo

‘I found the FOI training session to be highly informative and well-structured. It covered all the key areas comprehensively and provided clear, practical guidance throughout. The content was easy to follow, and the delivery by Gary was engaging, making complex topics accessible and understandable’. 

‘The training session has really helped me to understand the IG rep role a bit more and what I need to be thinking about when receiving a request for information’. 

Charlene Haynes & Team
Tendring District Council
dyslexia-action-logo-client

“I have worked with the Data Protection People for some time now. Their expertise has been drawn upon to assist us with our GDPR compliance gap analysis project, ROPA design and production through to conducting objective reviews and surveys. They are always available to help us out and their advice and guidance is excellent and delivered in a timely way. Special mentions to Kathy Midgley, Phil Brining, and David Hendry. A great, reliable and dependable service!”

Judy Barker
Dyslexia Action
Veritau client

“A great service and peace of mind. Data Protection People provides a well-rounded service to ensure customers are fully supported in their approach to GDPR compliance. My interaction has largely been with the following people: Kathy Midgley – another great asset to the organisation. Always approachable, always helpful and consistently supportive to the team and customers.

Julie Ferguson
Veritau
Woodgate & Clark

“We have been working with the Data Protection People for many years now, and have found them to be insightful, helpful, and knowledgeable in all areas of Data Protection Compliance. Data Protection People have taken the time to understand our business, the regulatory environment we sit under, and the unique challenges we face in the industry. They have supported us in all areas of Information and Data Security, assisting in assessments of our policies and changes to our processes. They are always willing to go the extra mile and prioritise support where required.”

Nia Roberts
Woodgate & Clarke

Data Protection People Blogs & Podcasts

Data Privacy Learning & Guidance

Data Protection People have the UK’s #1 Data Protection Podcast with over 250 episodes available across all audio streaming platforms, we also post regular content designed to simplify complex areas of data protection and cyber security, check out some of the podcasts and articles below and make data protection easy today.

Weaponised Subject Access Requests: How to Respond

What Is a Weaponised Subject Access Request?

A “weaponised” Subject Access Request (SAR) is a SAR that is being used as part of a wider dispute or strategy, rather than simply because someone wants to understand what personal data an organisation holds about them.

You often see this during a grievance, disciplinary process, redundancy consultation or employment dispute. Someone might use a SAR to find out what has been said about them internally, gather information about how decisions were made, or obtain material they think could support their position.

However, this is still a SAR…

The motivation behind the request does not automatically make it invalid, and an organisation cannot simply refuse to deal with it because it believes the individual is trying to gain an advantage in a dispute. The term “weaponised” describes how the SAR may be being used but it does not remove the individual’s legal right of access to their personal data under UK GDPR.

That distinction matters: when a SAR lands in the middle of an already difficult situation, it can be tempting to see it as part of the dispute and look for a reason not to respond and that is where organisations can get themselves into trouble.

The better approach is to recognise the wider context, understand exactly what the individual is asking for, and handle the SAR properly.

How to Spot It

There is no definitive test, but there are some patterns we see regularly here in DPP:

  • Timing: the SAR arrives immediately after a grievance is raised, disciplinary action begins, redundancy is discussed or another dispute develops.
  • Scope: the individual asks for “everything” about them, every email, Teams message, note, document or conversation in which they are mentioned.
  • Target: the wording focuses heavily on communications involving a particular manager, colleague or decision-maker.
  • Purpose: the request appears designed to uncover internal discussions, opinions or information connected with a separate dispute.
  • Pattern: the individual submits repeated or overlapping SARs, sometimes shortly after an earlier request has been completed.

None of these things automatically makes a SAR invalid, excessive or something you can refuse! They are simply signs that context matters. A broad request made during an employment dispute may be frustrating and time-consuming, but that does not mean an organisation can dismiss it as “weaponised” and move on.

From experience, the real question in this scenario is not “can we get out of responding to this?” but “how do we respond properly and proportionately?”

We break down real examples and the practical challenges organisations face in Weaponised SARs: A Growing Challenge for Organisations, the first episode in our series on this topic.

What Changed Under the Data (Use and Access) Act 2025?

The Data (Use and Access) Act 2025 (DUAA) introduced some useful changes to how organisations can deal with SARs, particularly when requests are very broad or difficult to manage.

You Don’t Have to Search Absolutely Everywhere

The law now makes it clear that organisations only need to carry out searches that are reasonable and proportionate. This doesn’t mean you can ignore parts of a SAR because they are difficult or time-consuming. But it does mean you are not expected to carry out endless searches where the effort involved would be unreasonable compared with the information you are likely to find.

This can be particularly helpful with very broad SARs asking for things like “every email, message, note and document that mentions me”.

The important thing is to make a sensible decision about what should be searched and keep a record of why.

You Can Ask for Clarification and Pause the Clock

If a SAR is so unclear that you genuinely can’t tell what the person is looking for, you can ask them to clarify their request and while you are waiting for their answer, the response clock can be paused.

But you can’t use clarification simply as a way to buy more time or force someone to make their SAR smaller! There needs to be a genuine reason for asking.

If you reasonably need proof of identity, the timing works slightly differently. The one-month response period does not start until you have received the information you need to confirm who the person is.

You Still Normally Have One Month to Respond

The basic deadline hasn’t changed: you normally have one month to respond to a SAR. In some cases, you can extend this by up to a further two months if the request is complex or the person has made several requests.

The DUAA hasn’t given organisations a way to simply reject difficult or weaponised SARs but what it has done is give organisations clearer tools to manage them properly.

The message is simple: you still have to deal with the SAR, but you don’t have to make the process harder than it needs to be.

We discussed these changes and answered practical questions about difficult SARs in Weaponised SARs Part 2: Live Discussion and Q&A.

How to Respond to a Weaponised SAR, Step by Step

A difficult or weaponised SAR still needs to be handled properly: the key is to stay organised, keep the request focused and record the decisions you make along the way.

Understand What They Are Actually Asking For

The first step should be to read the request carefully and understand what information they are looking for. Is there a particular person, decision, period of time or issue they are interested in?

If the request is unclear and you genuinely need more information to understand what they want, you can ask them to clarify it. The response clock can be paused while you wait for their answer. But a broad request does not automatically give you a reason to ask for clarification, and you cannot force someone to narrow their SAR just because it would make it easier to deal with.

Check Their Identity, Where Necessary

You need to be satisfied that the person making the SAR is who they say they are. That does not mean asking everyone for a passport or driving licence. Any identity checks should be reasonable and proportionate to the circumstances. Nevertheless, if you genuinely need more information to confirm their identity, the one-month response period does not start until you receive what you need.

Search Where the Information Is Actually Likely to Be

Organisations do not need to search every system in the organisation just in case something might be there: it is important to focus on the places where the person’s information is reasonably likely to be found. That could include particular mailboxes, Teams messages, HR systems, shared folders or other relevant records.

The search needs to be reasonable and proportionate, and you should be able to explain why you chose the areas you searched.

Review the Information Properly

Finding a document does not automatically mean the whole document needs to be disclosed. You may need to remove information about other people or apply one of the legal exemptions available under data protection law.

The important thing is to apply redactions and exemptions carefully and consistently. This is the stage our SAR Support team deals with every day, including requests involving thousands of pages of information.

Decide How You Are Going to Respond

This is a very important step! In most cases, you will respond to the SAR and provide the information the person is entitled to receive, with any necessary redactions or exemptions applied.

In some cases, you may consider refusing all or part of the request, or charging a reasonable fee, because it is manifestly unfounded or excessive. That is a high bar. As we could see from our last episode on the podcast, a request is not excessive simply because it is large, inconvenient or arrives during a difficult dispute. You need to look at the circumstances of the individual request and be able to justify your decision.

Keep a Record of Your Decisions

Document what you did and why. It is essential that you keep a record of the searches carried out, any clarification requested, the exemptions applied, the reasons for redactions and any decision to refuse or charge a fee. If the requester later complains, or the ICO asks questions, you should be able to show how you reached your decision.

Common Mistakes to Avoid

Some of the biggest problems we see are actually quite simple:

  • Ignoring the SAR because it looks tactical. Whatever the person’s motivation, it may still be a valid SAR.
  • Missing the deadline. A difficult grievance or employment dispute does not stop the SAR clock.
  • Searching absolutely everywhere. Focus on reasonable and proportionate searches instead.
  • Redacting inconsistently. Similar information should be treated in a consistent way.
  • Refusing a request simply because it is large. Size alone does not make a SAR excessive.
  • Failing to record your reasoning. If you cannot explain why you made a decision, it becomes much harder to defend later.
  • Leaving the review entirely to people involved in the dispute. Where possible, involve someone who can look at the information objectively, particularly where the SAR is sensitive or contentious.

The aim is not to “beat” a weaponised SAR. It is to stay in control of the process, apply the law properly and avoid creating another problem on top of the dispute you already have.

Do You Need Outside Help?

Not every difficult SAR needs outside support. Many can be handled perfectly well in-house. But weaponised SARs often arrive at the worst possible time: there is already a dispute underway, relationships may be strained, large amounts of information need to be reviewed, and the SAR deadline is still running in the background. Outside support can be particularly useful where:

  • The request involves a large amount of information.
  • The people who would normally handle the SAR are involved in the underlying dispute.
  • Significant redaction or exemptions are likely to be needed.
  • Internal teams simply don’t have the time or capacity to deal with it.
  • You want an independent pair of eyes on a particularly sensitive request.

The important thing is knowing when a SAR is becoming too difficult or time-consuming to manage alongside everything else.

Our SAR Support team can help with the process, from supporting searches and reviewing documents through to redaction and preparing the final response. This can help keep the SAR organised, consistent and separate from the wider dispute.

We’ve also covered weaponised SARs across three episodes of our podcast, looking at real scenarios and the practical issues organisations face:

If you’d rather have a specialist team handle a request like this directly, that’s exactly what our SAR Support service is built for.

Frequently Asked Questions

Is a Weaponised SAR Still Legally Valid?

Yes. The fact that someone makes a SAR during a dispute, grievance or legal claim does not make it invalid. You still need to deal with it as a SAR and follow the normal rules.

Can We Refuse a Weaponised SAR?

Not simply because you think it is being used strategically. You may be able to refuse all or part of a request if it is manifestly unfounded or excessive, but this is a high bar. You need clear reasons for the decision and should keep a record of how you reached it.

What Changed Under the Data (Use and Access) Act 2025?

The Act made it clear that organisations only need to carry out reasonable and proportionate searches when responding to a SAR. It also introduced clearer rules around asking for clarification. If you reasonably need more information to understand what the person is asking for, the response clock can be paused while you wait for their answer.

If you reasonably need information to confirm someone’s identity, the one-month response period does not start until you receive it.

How Long Do We Have to Respond?

Normally, one month. The deadline can be extended by up to a further two months where necessary because of the complexity or number of requests. If you are extending the deadline, you need to tell the requester within the first month and explain why.

Do We Have to Disclose Information About Other Employees?

Not necessarily. A document can contain both the requester’s personal data and information about somebody else. You need to consider the rights of both people before deciding what can be disclosed. Sometimes this means redacting the other person’s information. In other cases, it may be reasonable to disclose it. It depends on the circumstances.

Should We Handle a Weaponised SAR Internally or Get Outside Support?

Either can work. If you have the time, experience and resources to handle the SAR properly, there is nothing wrong with dealing with it internally. Outside support can be useful where the request is particularly large or sensitive, your team is already stretched, or the people who would normally deal with the SAR are involved in the underlying dispute.

The important thing is making sure the request is handled fairly, consistently and on time.

Does Someone Have to Tell Us Why They Are Making a SAR?

No. Someone does not normally need to explain why they want access to their personal data. Even if you believe the SAR is connected to a grievance, employment dispute or legal claim, you still need to deal with the request properly.

Can We Ask Someone to Narrow Down a Very Broad SAR?

You can ask, but you cannot force them to make their request smaller just because it would be easier for you to deal with. If you genuinely need clarification to understand what information they are asking for, you can ask for it and, where the legal requirements are met, pause the response clock while you wait.

Is a Very Large SAR Automatically Excessive?

No. A request is not excessive simply because it involves a lot of emails, documents or other information. You need to look at the circumstances of the request before deciding whether it is manifestly excessive.

What If the SAR Asks for Every Email That Mentions the Person?

You still need to carry out reasonable and proportionate searches, but that does not necessarily mean searching every mailbox and system across the organisation. Think about where the person’s information is actually likely to be held, who is likely to hold it and what searches are reasonable in the circumstances.

Do We Have to Provide Every Document We Find?

No. A SAR gives someone the right to access their personal data, not necessarily every document that contains their name. You need to review what you find and decide what personal data the person is entitled to receive, whether information about other people needs to be protected and whether any exemptions apply.

What If the SAR Is Connected to an Employment Tribunal or Legal Claim?

The existence of a separate legal dispute does not remove someone’s right to make a SAR. You should deal with the SAR under the data protection rules while also considering whether any exemptions apply to particular information, such as information covered by legal professional privilege.

Can We Charge Someone for Making Repeated SARs?

Not automatically. SARs are normally free. In some circumstances, you may be able to charge a reasonable fee where a request is manifestly unfounded or excessive, including where its repetitive nature makes it excessive. You need to be able to justify that decision.

Can Someone Make Another SAR After We Have Already Responded to One?

Yes. There is no general rule preventing someone from making another SAR. However, if requests become repetitive or overlap heavily with requests you have already answered, that may be relevant when considering whether a new request is manifestly excessive.

What Happens If We Miss the SAR Deadline?

Don’t ignore it just because the deadline has passed. Complete the response as soon as possible, keep a record of what caused the delay and consider whether you need to improve your process. The individual can complain to the organisation and may also raise the matter with the ICO.

Should HR Deal With a Weaponised SAR If It Relates to an Employee Dispute?

HR can be involved, particularly because they may know where relevant information is held, but the SAR should still be handled as a data protection request. Where HR staff are directly involved in the dispute, it can be sensible for someone else to oversee the review and decisions around disclosure, redaction and exemptions.

Next Step

A weaponised SAR is manageable when it’s handled properly and on time. If one has landed on your desk, or you want your process ready before it does, get in touch with our SAR Support team.
What Cyber Security Consultancy Actually Covers

Cyber security consultancy is independent expert advice on identifying, prioritising and managing your organisation’s information security risk. Rather than a single product or a fixed technical check, it’s guidance shaped around your actual business, what data and systems you have, what threatens them, and what a sensible, proportionate response looks like.

What a cyber security consultant actually does

A consultant’s work typically starts with understanding what you have and what matters most, your critical systems, your data and where the real exposure sits. From there, the work usually covers risk assessment, identifying and prioritising the threats most relevant to your organisation, policy and process development, building the governance that sits behind good security practice, incident response planning, so you know what happens if something does go wrong, and ongoing advice as your organisation, your systems, and the threat landscape all change over time.

Consultancy versus a specific technical service

It’s worth being clear about how this differs from a named technical service like penetration testing or ISO 27001 certification. Those are specific, defined pieces of work with a clear scope and a clear output, a test report, a certificate. Consultancy is broader and more advisory, it often points toward those specific services as part of a wider plan, rather than being one itself. A good consultancy engagement will usually tell you which specific technical work, if any, you actually need, rather than assuming you need everything.

Why organisations bring in a consultant rather than handling security internally

Few organisations outside large enterprises have a dedicated, senior security specialist on staff, and cyber security is a genuinely broad field, technical controls, governance, regulatory obligations, and incident response all draw on different expertise. Bringing in a consultant gives you access to that breadth without the cost of building an internal security function from scratch, and it gives you an independent perspective, someone assessing your risk without the internal politics or blind spots that can affect how an organisation sees its own weaknesses.

What a good consultancy engagement should produce

You should come away from a proper consultancy engagement with a clear picture of your actual risk, not a generic list of best practices, a prioritised set of recommendations that reflects what genuinely matters for your organisation rather than everything technically possible and a realistic view of cost and effort, so decisions can actually be made and acted on rather than filed away. If an engagement doesn’t leave you able to explain your top three security risks and what you’re doing about them, it hasn’t done its job.

Questions organisations usually ask before bringing in a consultant

How is a consultancy engagement usually priced? Most commonly either a fixed fee for a defined piece of work, a risk assessment with a report and recommendations, or day-rate work for more open-ended engagements. A good consultant scopes this with you upfront so cost is clear before work starts, rather than becoming open-ended once underway.

Will a consultant just tell us to buy expensive technical solutions? A good one won’t. The point of independent consultancy is a recommendation shaped by your actual risk and budget, not a sales process for a particular product or vendor. If every recommendation happens to point toward one specific tool, that’s worth questioning.

Do we need consultancy if we already have an IT provider? Often yes, and the two aren’t the same thing. An IT provider typically keeps systems running and supported, which is necessary but different from an independent assessment of security risk and governance. Many organisations use consultancy specifically to get a view that isn’t shaped by whoever also benefits commercially from the technical decisions made afterward.

What if the consultant finds something serious straight away? A properly run engagement flags anything urgent immediately, rather than waiting for a final report, so you can act on genuine risk as soon as it’s identified rather than sitting on it for weeks while the rest of the assessment continues.

When to bring in cyber security consultancy

The most common triggers are a specific event, a near miss, an incident at a similar organisation, a new client or contract that expects evidence of good practice, a genuine unknown, uncertainty about where your actual exposure sits, or a planned change, a new system, a merger, or expansion into a new market that changes your risk profile. It’s also worth treating security as an ongoing conversation rather than a one-off project, threats and systems both change, and a consultancy relationship that continues past the first engagement tends to catch problems earlier than a single audit ever could.

If you want an honest, independent view of where your organisation’s cyber security risk actually sits, our Cyber Security Consultancy service is built to give you exactly that.

ISO 27001 Certification: What’s Actually Involved

ISO 27001 is the international standard for an Information Security Management System, or ISMS. It’s not a single technical control or a piece of software, it’s a structured framework for how an organisation identifies its information security risks, decides how to manage them, and proves it’s actually doing so consistently.

What an ISMS actually is

An ISMS is the set of policies, processes, and controls an organisation puts in place to protect the confidentiality, integrity and availability of its information. ISO 27001 doesn’t tell you exactly which technical tools to buy, it tells you how to build a management system that identifies your actual risks and applies proportionate controls to them, then keeps reviewing whether those controls are still working.

The certification process

Getting certified to ISO 27001 involves building the ISMS itself, running a risk assessment across the organisation, implementing the controls that risk assessment points to, and then going through an external audit carried out by an accredited certification body. The audit typically happens in two stages, a review of your documentation and readiness, followed by a more detailed assessment of whether the ISMS is genuinely operating as described. Certification isn’t permanent, it’s maintained through ongoing surveillance audits, usually annually, with full recertification typically every three years.

Annex A and the control set

ISO 27001 includes a reference set of controls, known as Annex A, covering areas like access control, physical security, supplier relationships, incident management and business continuity. Not every control applies to every organisation, part of the process is justifying which controls are relevant to your specific risks and which genuinely aren’t, documented in what’s called a Statement of Applicability.

Why organisations pursue it

A few reasons come up consistently. Certification is increasingly a requirement to win or retain contracts, particularly with larger clients, public sector bodies and organisations that handle sensitive data through their supply chain, since it gives a third party independent evidence of your security posture rather than just your own word for it. It also forces a level of internal discipline that many organisations wouldn’t otherwise get around to, a proper risk assessment, clear ownership of security decisions and a documented incident response process. For organisations already required to demonstrate strong data protection practices, having a recognised ISMS in place makes it considerably easier to evidence that seriously.

ISO 27001 versus other cyber security standards

It’s worth being clear about how ISO 27001 differs from other things it sometimes gets confused with. Cyber Essentials is a narrower, UK government-backed scheme focused on a specific set of technical controls, it’s faster and cheaper to achieve but covers considerably less ground than a full ISMS. PCI DSS is specific to organisations handling payment card data. ISO 27001 is broader than either, covering the management system around information security generally, not just a fixed technical checklist or a single type of data.

Questions organisations usually ask about ISO 27001

How long does certification usually take? For most small and mid-sized organisations, building the ISMS and getting through both audit stages typically takes several months, largely driven by how mature your existing documentation and controls already are, not just the size of the organisation. Starting from close to nothing takes considerably longer than formalising practices that already exist informally.

Do we need to certify the whole organisation, or can we scope it to part of the business? You can define the scope of your ISMS deliberately, certifying a specific department, service line, or set of systems rather than the entire organisation, provided that scope is clearly documented and genuinely reflects where the relevant risk sits. Many organisations start with a narrower scope and expand it over time.

What’s the difference between ISO 27001 and Cyber Essentials in practical terms? Cyber Essentials is faster, cheaper, and covers a fixed set of technical controls, a good baseline. ISO 27001 is a full management system covering governance, risk assessment, and a much broader control set, verified by external audit rather than self-assessment. Many organisations hold both, Cyber Essentials as a baseline and ISO 27001 as the more comprehensive standard clients and larger contracts increasingly expect.

What happens if an audit finds a nonconformity? It’s not an automatic failure. Auditors typically distinguish between minor nonconformities, which you address within an agreed timeframe while keeping certification on track, and major ones, which need resolving before certification is granted. A well-prepared organisation usually finds and fixes the significant gaps itself before the external audit ever happens.

Is ISO 27001 right for your organisation

Certification makes most sense for organisations that handle sensitive or high-volume data, operate in sectors where clients or regulators expect independent assurance, or are regularly asked by procurement processes to prove their security posture. For smaller organisations without those pressures, the investment of time and cost needs weighing against the actual demand for it from your clients and market. The starting point either way is usually the same, a proper gap analysis against the standard, so you know exactly what you’d need to build before committing to the certification process itself.

If you want to understand where your organisation currently stands against ISO 27001, or you’re ready to start the certification journey properly, our ISO 27001 service is built to guide you through it.

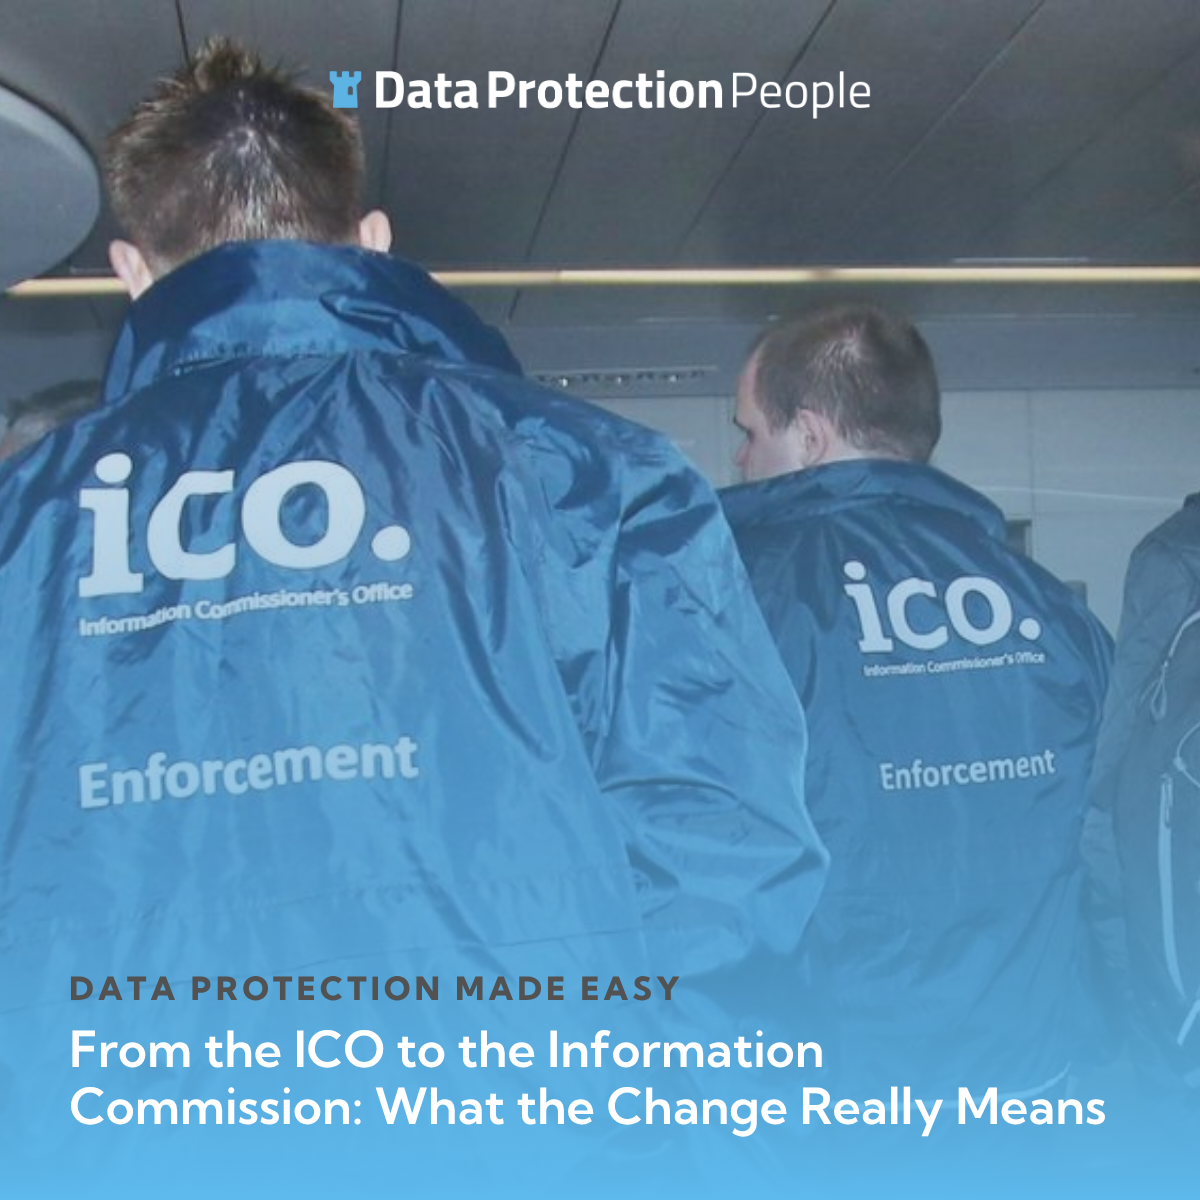
From the ICO to the Information Commission

With the Information Commissioner’s Office (ICO) transition to the “Information Commission” under the Data (Use and Access) Act (DUAA) 2025 set to be confirmed on 30 September 2026, it is an appropriate moment to look at what this change actually means for the regulator.

The transition is a structural evolution that will not change the fundamental role and responsibilities of the regulator. The DUAA amends references to “Information Commissioner” to the “Information Commission,” so all existing functions transfer over. The commencement regulations also ensure that actions taken by, or in relation to, the Information Commissioner before 30 September 2026 will continue to have effect after the transfer to the Information Commission.

It is fair to classify the transition as more administrative than substantive, especially from the perspective of organisations. For organisations, the change may involve nothing more than updating documentation to refer to the Information Commission. However, the transition represents more than a rebrand. The way the regulator is constituted, governed and held to account is genuinely changing.

The narrative around the DUAA changes often focuses on the perspective of organisations, reduction in regulatory burden, simplification of certain requirements and greater flexibility to process personal data. But what is the view from the regulator’s side, and what, if anything, can those subject to its authority expect to change?

Towards Board Governance

Moving from a governance structure built around a corporation sole (the Information Commissioner) to a body corporate (the Information Commission) modernises the UK’s data protection regulator, bringing it into alignment with other domestic regulators such as Ofcom and the Competition and Markets Authority (CMA).

Whilst the Information Commissioner had the final say in decision making, the Information Commission will operate with a board comprising the Chair of the Information Commission, a chief executive officer, and other non-executive and executive members who will share decision-making responsibilities.

In July 2026 the appointment of seven Non-Executive Members to the Information Commission Board was announced, Laurie Benson, Maggie Carver, Stephen Cohen, Sukhvinder Kaur-Stubbs, Gary Kildare, Hilary Newiss and Scott McPherson, alongside the launch of recruitment for the Chair of the Information Commission. The appointments are intended to give the new Board a wider range of skills and experience across business, technology, regulation, governance and public service, embedding strategic leadership and oversight within a collective governance structure.

The impact of this structural change will be to make the regulator less personality-led and more framework-led. A corporation sole should, in theory at least, offer decisiveness, but as we have seen, it is also liable to make regulatory tone and emphasis dependent on one individual’s instincts, leading to data protection laws “varying with the length of the Commissioner’s foot.”

Data protection regulation in the current age requires not just authority, but governance, oversight and expertise. A board structure brings all three, as well as greater resilience, continuity in strategy and a broader range of perspectives. Having a wider range of views factored into the regulator’s approach aligns with the formal expansion of the ICO’s regulatory priorities under the DUAA.

Beyond Protecting Personal Data

The DUAA introduces a fresh strategic framework for the regulator when carrying out its functions, built around a principal objective supported by several other key areas. The primary duty remains to secure an appropriate level of protection for personal data, alongside a new additional requirement to promote public trust and confidence in the processing of personal data.

The other factors set out in the DUAA, which the Commission must have regard for when carrying out its tasks and responsibilities, are not new priorities as such but existing areas of focus for the ICO that now gain formal recognition and reinforcement within the Commission’s overall remit, including:

  • The desirability of promoting innovation
  • The desirability of promoting competition
  • The importance of the prevention, investigation, detection and prosecution of criminal offences
  • The need to safeguard public and national security
  • The fact that children merit specific protection with regard to their personal data

This broadening of the regulatory remit reflects the fact that the data protection regulator’s role is no longer confined to data breaches and individual rights, but increasingly involves supervision across emerging areas of public concern such as artificial intelligence, children’s data, biometrics, online tracking, cross-regulatory coordination and the relationship between data protection, competition and innovation.

Alongside this expanded focus is a duty for the Commission to consult other regulators on economic growth, innovation and competition, which will presumably take place through the existing DRCF (Digital Regulation Cooperation Forum), which brings together the ICO, the Financial Conduct Authority (FCA), Ofcom and the CMA.

This signals a move away from data protection being treated as a standalone compliance issue and toward a more joined-up regulatory model, in which privacy, competition, innovation and online safety are assessed alongside one another. In practice, this increases the likelihood of coordinated regulatory expectations, shared intelligence and scrutiny across regulators, meaning organisations may face a more consistent but also more demanding regulatory environment.

The Commission will be held accountable for this new remit by greater transparency requirements introduced by the DUAA, which require it to publish an annual analysis of its performance and report on regulatory action, including the nature of investigations, time taken and powers used. Requiring the regulator to explain not only what it prioritises but how efficiently it uses its powers and resources is intended to create a more publicly accountable institution.

Alongside factoring these considerations into its decision making, the Information Commission will also have a range of DUAA changes to oversee, each motivated by these same considerations. The changes around automated decision making and the scientific research exemption clearly reflect the promotion of innovation and competition. The recognised legitimate interest for sharing data for crime prevention and national security reflects the crime-based objective, and children’s data reforms, which embed children’s higher protection considerations more firmly into regulatory expectations, reflect the associated aim.

This combination of new regulatory considerations also shows up in the regulator’s prominent priorities for 2026, which include the AI and biometrics strategy, and the Children’s Code and its enforcement guidance. This broader remit will clearly come to permeate the Information Commission’s work across the board. So how is it likely to show up in future enforcement action?
The Enforcement Forecast

The ICO’s recent enforcement track record has remained broadly aligned to the primary objective of protecting personal data, data rights and upholding public trust, with many headline sanctions relating to data security breaches, including the Capita, Advanced Computer Software, 23andMe and LastPass fines.

However, recent action taken against TikTok and Reddit, centred on proactively protecting children’s data, points to the ICO broadening its focus beyond data security breaches, reflecting the wider regulatory priorities formalised by the DUAA. Children’s data is best viewed not as one priority among many, but as an increasingly cross-cutting theme across all the newly formalised regulatory priorities.

Whether the enforcement picture will change following the increased monetary penalties for PECR breaches, which bring this regime in line with the UK GDPR, is debatable. The clear point to make is that PECR can no longer be treated as a poor relation of the UK GDPR and should attract the same level of compliance focus.

However, there is a valid observation that PECR fines tend to be imposed against cold callers and those operating in flagrant disregard for the requirements, often lacking the financial means to meet fines imposed under the previous £500,000 threshold, let alone fines within UK GDPR limits.

It is likely that the threshold increase is focused on deterrence, with the original threshold not providing enough of one. Whilst it is debatable whether the ICO will issue significantly larger PECR fines than before, it is worth bearing in mind that historically more fines have been issued under PECR than the UK GDPR, partly because PECR breaches are more straightforward for the regulator to evidence.

The overall trend of enforcement action in recent years, despite the ICO’s public sector approach, has been upward, and it is likely to continue on this trajectory, especially given the new enforcement procedural guidance set to replace the 2018 Regulatory Action Policy, which will determine how the ICO operates in view of the expanded powers conferred by the DUAA.

In particular, the introduction of structured settlement procedures akin to those used by the FCA and Ofcom, offering discounts to fines of up to 40% for early resolution before a notice of intent, 30% after notice of intent and 20% after written representations, points to a regulator keen to settle cases quicker, avoid time-consuming litigation and free up capacity for further enforcement. These priorities are also furthered by new evidence gathering powers.

Enhanced Evidence Gathering

The headline new evidence gathering capabilities conferred on the ICO, and soon the Information Commission, under the DUAA are powers to:

  • Compel production of specific documents (in force since 19 August 2025)
  • Compel a witness to attend an interview (in force since 5 February 2026)
  • Request technical reports

These powers strengthen the regulator’s evidence gathering tools in response to investigative challenges. The first clarifies the regulator’s existing power to issue Information Notices, ensuring this expressly includes specific documents. The second allows the regulator to compel anyone working for the controller or processor, currently or previously, to attend an interview, removing reliance on voluntary interviews.

The first two powers are likely to be used primarily to deal with uncooperative respondents. A regulator having to use these powers at all is likely to be treated as an aggravating factor when sanctions and penalties are decided. However, it is the third power that is the most eye-catching, and likely the most impactful for the regulator, data subjects and organisations alike.

For the regulator, the power to mandate production of a report by an approved person, at the cost of the organisation and with specific subject matter, form, manner and date of preparation, should free up capacity to investigate and sanction more organisations. This is especially true given this power is likely to be used for technical and cyber-related matters, which are particularly resource and time intensive for the ICO.

These reports also have the potential to become more easily available to claimants than other internally produced equivalents, and could be highly advantageous for advancing legal claims. This is worth considering given the rise in the UK of collective and representative data breach claims, and the fact that the ICO appears content with data subjects placing increasing pressure on organisations.

Complaints: Lightening the Regulator’s Burden

The overall intention of the DUAA complaints changes (full article here) is not only to increase the obligation on organisations to resolve data protection complaints raised by individuals, but in turn to reduce the burden placed on the ICO by the large volume of complaints made to it directly. This is being achieved by:

  • Giving individuals the legal right to raise data protection complaints with organisations directly, where previously they only had the legal right to complain to the ICO
  • Requiring organisations by law to facilitate and address data protection complaints made directly to them, rather than this being merely a regulatory expectation
  • Allowing the ICO to defer individuals and organisations until the organisation’s own complaints process is exhausted and regulatory involvement is warranted

Alongside the DUAA complaints changes, the ICO has published a new framework on how it handles complaints, aimed at more effectively managing the large and increasing volumes it receives. There is also an intention to further use complaint data, both the ICO’s own and that which it can now also request from organisations following the DUAA, to help identify broader issues with organisational compliance and inform regulatory interventions.

The overall aim of the framework is to focus resources on cases where the ICO can have the biggest impact and where issues align with strategic priorities, reinforcing the message that the regulator cannot act on every complaint. This has long been an aspiration, and the regulator will hope it becomes far more achievable following the DUAA changes. Whether this actually changes the picture for a cross-sector regulator that has tended to become overrun by complaints remains to be seen, though the intention is clearly to free up and better target resources toward key, impactful issues.

Conclusion

The government and the ICO have presented the DUAA as a reform package focused on promoting innovation, supporting growth and making compliance easier for organisations. There is truth in that, the Act relaxes and clarifies certain requirements, for example around scientific research, recognised legitimate interests, cookies and automated decision-making. But the transition to the Information Commission shows that simplification is only half the story.

The other half is a regulator designed to be more strategically oriented, better equipped and more assertive in its regulatory action. Organisations taking advantage of the greater flexibility permitted by the DUAA should be mindful that this freedom comes with a string attached: the regulator is better equipped to investigate and penalise should things go wrong. In that sense, the regulatory environment may have become easier to understand in some areas, but not necessarily easier to navigate.

Ultimately, this is not a shift from more regulation to less, but from an older model of data protection oversight to a newer version that is board-governed, strategically accountable and more appropriately calibrated for the emerging pressures of AI, digital markets, children’s privacy and an increasingly sophisticated enforcement picture. That is the real significance of the move from the ICO to the Information Commission.

S2 Ep32: GDPR Radio- Data Protection News Of The Week

S2 Ep32: GDPR Radio – Data Protection News of the Week

Caine Glancy and Amber Sivill discuss the latest developments affecting data protection professionals.

In this episode of the Data Protection Made Easy podcast, Caine and Amber examine several stories raising important questions about privacy, cyber security, artificial intelligence and accountability.

Their conversation covers proposed changes to UK data protection law, a cyber incident affecting airport customers, facial recognition technology, smart glasses, personal data breaches and online safety.

Could the UK Replace GDPR?

The episode begins with a discussion about reports that Reform UK wants to replace GDPR with a lighter-touch approach.

Caine and Amber consider whether data protection law genuinely prevents organisations from innovating. They also discuss what weaker enforcement and reduced individual rights could mean in practice.

Amber explains that GDPR is based on principles. This allows organisations to consider the purpose, necessity and risk involved in their processing.

“Whenever you look at anything within GDPR or data protection, it is always a matter of risk, what is proportionate to that risk and what is necessary.”

What Can Organisations Learn From the Airport Cyber Incident?

Caine and Amber discuss a reported cyber incident involving customer information collected through airport Wi-Fi registrations and car park bookings.

The conversation focuses on the volume of information affected, how connected systems can increase the impact of an incident and why organisations should only collect the personal data they genuinely need.

Amber also raises the importance of separating systems and databases. This is known as network segmentation, which means dividing a network into smaller sections to limit unauthorised access.

Should Retention Periods Be Based on Systems or Purposes?

The hosts explore whether organisations should assign retention periods to entire systems or connect them to individual processing purposes.

A single system may hold several types of personal data. Each type may be needed for a different reason and for a different length of time.

“Storage limitation is based on the purpose of processing and how long you require the information for that purpose.”

Amber explains that a more detailed approach can help organisations meet legal requirements and avoid retaining information for longer than necessary.

What Are the Risks of Automated Identity Checks?

The episode examines a case involving an eVisa identification problem which reportedly prevented a UK resident from boarding a return flight.

Caine and Amber consider the risks of relying on automated identity systems. These include inaccurate matches, a lack of effective human review and difficulties correcting errors.

They connect this discussion to the wider use of facial recognition by police forces and other organisations.

Smart Glasses, Facial Recognition and Covert Recording

Caine and Amber discuss smart glasses that can record people or use facial recognition technology.

Although this technology may support accessibility and language interpretation, it can also create privacy concerns when people do not know they are being recorded.

The hosts consider whether every function is necessary and whether useful features could operate without recording or identifying individuals.

Why Does Context Matter When Assessing a Data Breach?

The Metropolitan Police reportedly exposed the email addresses of people receiving updates about the investigation into Mohamed Al-Fayed.

An email address may appear low risk when viewed alone. However, the surrounding circumstances could reveal a connection to an investigation, witness group or affected individual.

“The context is ultimately so important with everything. It is a big decider when assessing risk.”

This example shows why organisations need clear breach-reporting processes. A proper assessment should consider who is affected, what the information may reveal and the possible consequences for those individuals.

Can Better Training Reduce Email-Related Breaches?

Caine and Amber discuss how simple email mistakes can lead to serious incidents, including using CC instead of BCC.

They explain that effective training should build awareness without making employees afraid to report mistakes or ask questions.

“If you do not know something, how do you know it is wrong?”

Staff need practical guidance, clear reporting routes and the confidence to raise concerns quickly.

Age Assurance and the Online Safety Debate

The episode closes with a discussion about age-assurance measures under the Online Safety Act.

Caine and Amber consider whether strict controls could push children towards less responsible websites. They also discuss the challenge of protecting children without creating systems that people simply try to bypass.

The discussion highlights the need for proportionate controls which protect users while recognising how people behave online.

Key Takeaways

  • Data protection law allows organisations to assess risk and act proportionately
  • Organisations should only collect personal data they genuinely need
  • Retention periods should reflect the purpose of processing
  • Automated identity systems need accuracy checks and effective human oversight
  • The context of a breach can make seemingly ordinary information highly sensitive
  • Training should help employees recognise and report mistakes without creating fear
  • New technologies need privacy safeguards from the beginning

Meet Your Hosts

Caine Glancy

Caine is the Data Protection Support Desk Manager at Data Protection People. He brings practical insight from supporting organisations with their everyday data protection responsibilities.

Amber Sivill

Amber joins Caine to examine the practical risks behind the latest data protection stories and explain what organisations should consider.

About the Data Protection Made Easy Podcast

The Data Protection Made Easy podcast turns complex privacy and data protection topics into clear, practical conversations.

GDPR Radio examines recent news, regulatory developments and emerging technology to help organisations understand what has happened and why it matters.

S2 Ep31: What Happens When Your DPO Is OOO?

S2 Ep31: What Happens When Your DPO Is OOO?

The hidden liability gap: what happens when your DPO leaves?

Your organisation’s data protection responsibilities do not pause when its Data Protection Officer is unavailable.

In this episode of the Data Protection Made Easy podcast, Caine Glancy and Gbenga Onojobi discuss how organisations can maintain accountability when their DPO is on annual leave, absent unexpectedly or has left the organisation.

The Latest Data Protection News

Before exploring the main topic, Caine and Gbenga discuss several recent stories from across data protection and technology.

  • The proposed use of live facial recognition at Scottish football matches
  • The importance of human review when automated systems identify people
  • Concerns about addictive features on social media platforms
  • Unauthorised access to patient records by a former NHS employee

The discussion highlights a recurring concern. Technology may support decision-making, but organisations still need appropriate oversight, accountability and safeguards.

Does Accountability Leave With the DPO?

A DPO may take annual leave, become unwell, resign or retire. An outsourced DPO arrangement may also come to an end. However, the organisation remains responsible for its data protection compliance.

“The DPO leaving or being out of office does not remove the organisation’s responsibility. Accountability does not leave with them.”

Gbenga compares the DPO to a navigator on a ship. The navigator advises on the route and watches for danger, but the captain and the organisation remain responsible for the journey.

Why Organisations Need a Continuity Plan

Organisations need to plan for temporary and permanent DPO absences. Staff should know who can provide advice, receive an escalation and take ownership of urgent work.

This is particularly important for matters with strict deadlines, including personal data breaches, subject access requests and other individual rights requests.

“Being able to have another trusted individual who helps you, whether that is upwards or downwards, is really quite vital.”

Policies and procedures should explain what happens when the usual DPO contact is unavailable. The plan may involve a deputy, trained managers, data champions or access to external data protection support.

Data Protection Is Not One Person’s Responsibility

Caine and Gbenga discuss the risks of allowing every data protection matter to sit with the DPO.

Senior leaders remain accountable. Managers and staff also need to understand how data protection applies to their work and when an issue must be escalated.

Training should reflect each person’s responsibilities. Board members, managers, data champions and frontline staff do not need identical training. They need practical knowledge that helps them recognise and manage the situations they may face.

Independence and Conflicts of Interest

When a DPO leaves, appointing the nearest senior employee may appear to solve the immediate problem. However, organisations must consider whether that person has the necessary expertise, time and independence.

A person should not be expected to make decisions about how personal data is used and then independently monitor their own decisions.

“Organisations should not solve a vacancy by creating an additional conflict. A rushed appointment may fill the box while leaving the organisation with a DPO who cannot properly perform the role.”

Protecting Time-Sensitive Work

A subject access request can arrive anywhere in an organisation. It may be sent to HR, reception, a manager or through social media. It may also be made verbally.

The individual does not need to use the words “subject access request” for the request to be valid. This means staff need to recognise a possible request and know where to send it, even when the DPO is unavailable.

Clear ownership and an appropriate quality assurance process can reduce the risk of missed deadlines, inappropriate disclosures or information being withheld incorrectly.

Questions to Ask Your Organisation

  • Who provides cover when the DPO is unavailable?
  • Do staff know where to send urgent data protection matters?
  • Who monitors subject access request and breach deadlines?
  • Are key decisions, risks and responsibilities properly recorded?
  • Does any temporary replacement have suitable expertise and independence?
  • Can the organisation access additional support when internal capacity is limited?

The Final Takeaway

“A DPO leaving an organisation should not create a compliance vacuum. The organisation itself remains accountable.”

Good continuity means recording important knowledge, clearly allocating responsibilities and making sure somebody suitable is ready to step in.

Meet Your Hosts

Caine Glancy

Caine is the Data Protection Support Desk Manager at Data Protection People. He brings practical insight from helping organisations manage everyday data protection questions, breaches and individual rights requests.

Gbenga Onojobi

Gbenga is a Data Protection Consultant at Data Protection People. He supports organisations with practical compliance, governance and data protection risk management.

Watch or Listen

📺 Watch on YouTube: https://youtu.be/hqokBvSh-Ho

🎧 Listen on Spotify: https://open.spotify.com/episode/7ukmE70eDsPsMYQG39O8kf

S2 Ep30: GDPR Radio – Data Protection News of the Week

S2 Ep30: GDPR Radio – Data Protection News of the Week

Practical discussion on the latest data protection news

In this episode of GDPR Radio, Caine Glancy and Catarina Santos discuss recent developments affecting data protection, workplace monitoring, media reporting and information security.

They explore the risks behind misleading headlines, AI systems that claim to detect employee emotion, smart glasses and a reported NHS data breach involving an unsecured pager network.

What This Episode Covers

  • A Court of Appeal decision on misleading headlines and the fair processing of personal data
  • Why images and headlines can shape public perception before people read the full story
  • AI emotion-detection tools and the risks of monitoring employees based on facial expressions, voice or body language
  • Why organisations must consider necessity, fairness, transparency and less intrusive alternatives before introducing workplace monitoring
  • Smart glasses, hidden recording and the need for clear acceptable-use policies
  • Lessons from a reported NHS pager network data breach
  • Why access controls, staff awareness and practical policies all matter

Key Discussion Points

“Someone who only saw the headlines and photographs together could just reasonably get the impression that actually it was Vince, the person that the article was referring to.”

The hosts discuss why data protection law can apply even where a full article clarifies the facts. The way a headline, image and article appear together can still affect whether personal data has been processed fairly.

“Could you not achieve the same objective with a completely less intrusive way?”

Caine and Catarina question the value of emotion-detection technology in the workplace. They explore why one-to-one conversations, objective work outputs and appropriate management may be more proportionate than analysing an employee’s voice, face or behaviour.

“Technical controls can only go so far, which is why the emphasis in the law is on technical and organisational measures.”

The episode also looks at why information governance needs to work in practice. Policies must reflect how an organisation operates, staff need to understand them and clear action needs to follow when rules are not followed.

Why This Episode Matters

Data protection risks do not always start with a major cyber incident. They can arise through misleading content, new workplace technology, weak access controls or policies that exist on paper but are not understood in practice.

This episode helps organisations consider where their own controls may need attention and why proportionate, people-focused

S2 Ep29: How AI Is Reshaping the DPO Role in 2026

S2 Ep29: How AI Is Reshaping the DPO Role in 2026

Data Protection Made Easy podcast with Caine Glancy and Amber Sivill

Artificial intelligence is changing how Data Protection Officers work.

AI tools can help with research, training, risk assessments and routine administration. However, they can also produce inaccurate advice, encourage confirmation bias and create new governance risks.

In this episode of the Data Protection Made Easy podcast, Caine Glancy and Amber Sivill discuss how AI is affecting DPO workloads and why professional knowledge and meaningful human oversight remain essential.

What Does This Episode Cover?

During the episode, Caine and Amber discuss:

  • The increase in AI-generated Subject Access Requests
  • How AI is affecting DPO workloads
  • The risks of using AI for data protection advice
  • How AI could support RoPAs, DPIAs and LIAs
  • The importance of checking AI-generated policies
  • Confirmation bias in AI responses
  • Why human oversight and professional knowledge still matter

How Is AI Affecting Subject Access Requests?

The discussion explored the growing number of Subject Access Requests, or SARs, that appear to have been generated using AI.

These requests can look formal and detailed. However, they may ask for information that does not fall within the normal scope of a SAR.

Amber explained:

“It also fuels a lot of misunderstanding. A lot of the time, you see a request and most of it does not even fall under the scope of what a SAR generally covers.”

Caine also shared that SAR-related cases handled through the DPP Support Desk have increased significantly.

AI may make it easier for people to create requests, complaints and follow-up correspondence. This can place additional pressure on data protection teams, particularly where requests are vague or based on incorrect information.

Can DPOs Rely on AI for Data Protection Advice?

AI can provide a useful starting point. However, it should not replace professional knowledge.

Amber explained:

“You need to have the base knowledge in order to be able to use these systems.”

An experienced practitioner may recognise when an AI response refers to the wrong legislation, misses important context or provides an answer that is too confident.

Someone with less experience may not spot those problems.

Data protection decisions are rarely black and white. The correct answer often depends on the organisation, the processing activity and the people who may be affected.

Could AI Support RoPAs, DPIAs and LIAs?

AI may help DPOs complete some routine or administrative tasks.

For example, it could help pre-populate a Record of Processing Activities, or RoPA, using information about an organisation’s activities and data sharing.

It may also provide a starting point for a Data Protection Impact Assessment, or DPIA, and a Legitimate Interests Assessment, or LIA.

However, organisations must consider what information they enter into an AI system. DPIAs and other assessments may contain sensitive or confidential information.

Amber said:

“There is a limit as to what you can provide the model with in terms of confidentiality and not oversharing any information.”

Any AI-generated assessment must be checked against the organisation’s actual processing, systems and risks.

Why Does Human Oversight Matter?

AI can produce clear and convincing answers even when those answers are incomplete or incorrect.

It may also agree with the direction of a prompt instead of challenging the user’s assumptions. This is known as confirmation bias, which means favouring information that supports an existing view.

Caine explained:

“It is a fantastic tool that will hopefully be able to help in the role as a DPO. But what matters is that you can supplement it with your pre-existing knowledge.”

Amber added:

“The human element needs to be someone overlooking it who actually knows what they are talking about.”

Human oversight must be meaningful. The person reviewing an AI output needs the knowledge and authority to identify problems, challenge the result and make the final decision.

Is an AI-Generated Policy Better Than No Policy?

An AI-generated policy is not useful simply because it exists.

A policy must reflect how the organisation actually works. It must be practical, accurate and followed by staff.

Amber explained:

“If you have a policy in place and it does not align with your business, it is not workable and people are not following it, then there is ultimately not really anything there in place anyway.”

AI may help structure a first draft. However, the final policy should be reviewed by someone who understands the organisation, its legal duties and its operational risks.

What Should DPOs Take Away?

AI can support DPOs, but it should not replace them.

Organisations should:

  • Use AI to support work rather than make final decisions
  • Check AI outputs against current law and ICO guidance
  • Avoid entering unnecessary personal or confidential information
  • Keep meaningful human oversight in place
  • Document how AI tools are approved, monitored and reviewed
  • Make sure policies and assessments reflect real business practices

The DPO role is becoming broader and more connected to technology, governance and organisational risk.

AI creates opportunities to work more efficiently. It also makes professional judgement, scepticism and accountability more important.

Meet Your Hosts

Caine Glancy

Caine is the Data Protection Support Desk Manager at Data Protection People. He works with organisations every day to help them understand and respond to practical data protection challenges.

Amber Sivill

Amber is a Data Protection Consultant at Data Protection People. She supports organisations with data protection compliance, governance and emerging technology risks.

Watch or Listen to the Episode

Watch the full episode on YouTube or listen on Spotify.

Watch on YouTube

Listen on Spotify

Need Support With AI Governance?

If your organisation is adopting AI, Data Protection Made Easy can help you understand the risks, strengthen governance and meet your data protection responsibilities.

Contact Our Team

Our Events & Webinars

Expert-led Discussions

We host events on a weekly basis for the community of data protection practitioners and have built up a network of over 1,700 subscribers. Members receive weekly invites, exclusive offers, early access to selected content, our monthly newsletter, and first access to in-person events. Check out our upcoming events and become part of our growing community.

View All
_GDPR Radio - Data Protection News of the Week
23 October 26 12:30 - 1:15 pm

S2 Ep40: GDPR Radio – Data Protection News of the Week

Why Most DPIAs Get Signed Off Too Late to Matter
16 October 26 12:30 - 1:15 pm

S2 Ep39:Why Most DPIAs Get Signed Off Too Late to Matter

Get Support With Data Protection And Cyber Security

Our mission is to make data protection and cyber security easy: easy to understand and easy to do. We do that through the mantra of benchmark, improve, maintain.